PHP Releases Emergency Fixes on Oct. 21 for 2 Critical Vulnerabilities
After issues each received a CVSS 4.0 score of 9.2, PHP’s development team moved up the release of fixes, and multiple services in Japan temporarily suspended operations or entered emergency maintenance. Applying the fixes remained the responsibility of each operator, while attempts to exploit the flaws surged around the time of their disclosure.
Both disclosed vulnerabilities were rated 9.2 under CVSS 4.0.1
Among websites whose server-side language is known, about seven in ten use PHP.2
Cloudflare reported that attempts to exploit the vulnerabilities reached the millions after their disclosure.6
Story
Why the Fix Release Coincided With Temporary SuspensionsPHP developers disclosed two critical vulnerabilities, each rated 9.2 under CVSS 4.0.1 CERT-EU identified the related issues as CVE-2026-109618 and CVE-2026-109619, warning that they could allow remote arbitrary code execution if exploited.3 The vulnerabilities could affect environments running PHP 5 and later, and depending on server configuration, could lead to code execution without authentication.23 Data theft and website defacement were also cited as possible impacts, though the actual risk depends on the configuration of each server.2
PHP initially planned to release the fixes at 11 p.m. Japan time on Oct. 21.1 The release time was moved up after information about the vulnerabilities began circulating online.1 Reports said the planned release was changed from 10 p.m. to between 10:30 and 10:40 p.m.1 Other reports said the decision was to release the fixes a day earlier than planned; the two accounts describe the move-up following the leak and the schedule change, respectively.12
The events leading to the fixes date back to an external security audit in 2024.1 That audit found an issue that pointed to one of the vulnerabilities now disclosed.1 The PHP team said it had been difficult to fix the affected memory-management and error-handling code, describing the delay in addressing it as a structural failure.1 In 2026, security work also made use of tools such as Claude Mythos and Daybreak Red, developed by OpenAI.1
Researchers at Calif reported a remote code execution issue, and OpenAI reported the same root cause on Aug. 11.1 According to the PHP Foundation, the issues centered on memory-management and error-handling code.1 Because that code is used in nearly every request, the issue was not limited to a particular feature.1 However, the breadth of environments potentially affected by the vulnerabilities is not the same as whether they can actually be exploited on each server; the latter depends on configuration.23
PHP is widely used on websites, and WordPress also relies on PHP.3 According to W3Techs, PHP is used by about seven in ten websites whose server-side programming language is known.2 That share is calculated among sites for which the language could be identified, and is not presented as a proportion of all websites.2 The widespread use helps explain why the response extended beyond individual technology companies to government, finance, transportation and consumer services.3
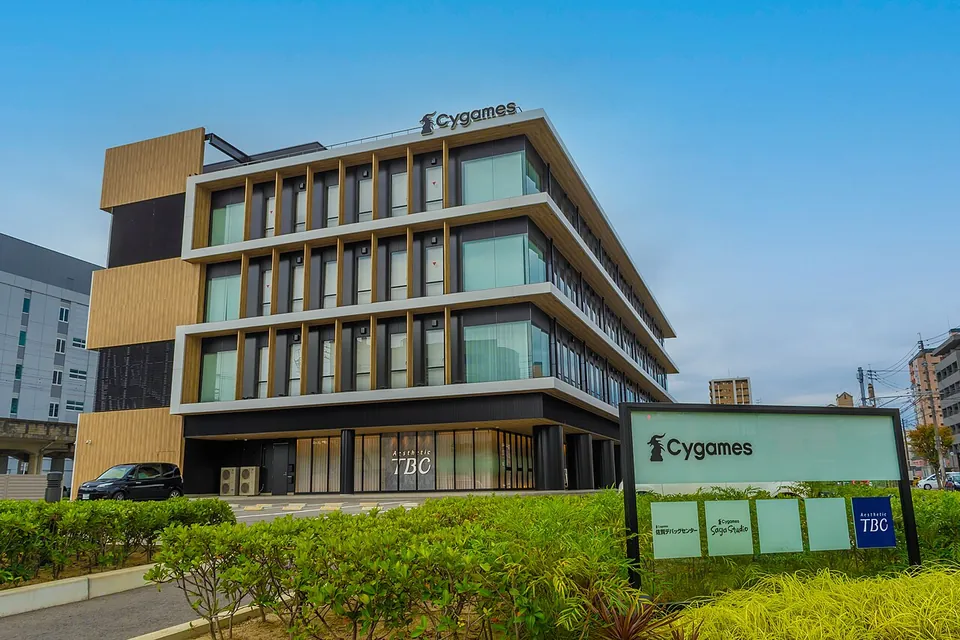
In Japan, Sakura Internet, Cygames and pixiv carried out emergency maintenance.3 Affected services also included BASE, niconico and DMM.com; games named included Granblue Fantasy and Umamusume: Pretty Derby.2 In finance and transportation, Nomura, MUFG, ANA and East Japan Railway temporarily suspended some internet services.6 The Ministry of Finance also temporarily suspended some website services, as a wide range of operators restricted access in different ways.236
Japan’s Information-technology Promotion Agency and National Cybersecurity Office issued warnings, and Prime Minister Sanae Takaichi urged operators to prepare promptly to apply the fixes.2 Takaichi said that if applying a fix immediately is difficult, temporarily suspending a website may help reduce risk.1 Takaichi’s official website was also taken offline while administrators addressed the issue, and was later restored.1 She also noted that website and server administrators play an important role because some operators may not notice warnings issued at night.1
Cloudflare reported observing thousands of exploitation attempts in the period before the vulnerabilities were disclosed.6 The number reached tens of thousands within 45 minutes of disclosure, then rose to hundreds of thousands soon afterward and eventually reached millions, the company said.6 The company also said it observed attacks targeting the vulnerabilities on the day they were disclosed.2 The sharp increase after disclosure is consistent with the authorities’ calls to speed up preparations for fixes and restrict access.1
The PHP development team released the fixes on Oct. 21, but each operator had to install them on its own systems.2 PHP users were urged to update promptly once the fixes became available.3 Software containing the patches had circulated more than 6 hours before the official release time.2 A demo video was also accidentally published, and copies continued to spread after it was deleted, making the management of information before release another factor that sped up the response.2 Applying the fixes closed the vulnerabilities, while temporary suspensions reduced exposure before they were installed; the two measures were separate parts of the short-term risk response.3 In Finland, government agency Valtori installed security updates overnight and gradually restored public websites.6
Structure
Who is connected to whom- 1PHP
- ← usesFact
- ← usesFact
- enables →Fact
- ← usesFact
- enables →Fact
History
How it came to this- 2024Related issue identified in an external auditThe audit found an issue pointing to one of the current vulnerabilities.
- August 11, 2026Report of the same root causeOpenAI reported the same root cause as a report by researcher Calif.
- October 21Patch release brought forward after information leakAs information about the vulnerabilities began to spread, PHP changed its release schedule and published patches.
- Now9.2 CVSS 4.0 ratings for critical PHP vulnerabilities
Impact
Spreading outward, level by level- Level 1Risk to servers
Depending on server configuration, the vulnerabilities could lead to unauthenticated code execution, data theft or website defacement.23
Fact - Level 2Broad adoption
PHP is widely used in websites, and WordPress also depends on it. The breadth of affected environments is considered one reason the response extended beyond technology companies.23
Fact - Level 3Japanese service operators
In Japan, multiple companies and services carried out emergency maintenance or temporarily suspended some services.236
Fact - Level 4Short-term risk reduction
Applying the patches closed the vulnerabilities, while temporary suspensions helped limit exposure before the patches could be applied.23
Fact
Sources
What each source supportsWritten by AI from the sources listed below: every fact was checked word for word against its source, and inference is marked apart. How we write